

Israeli firm: China cyber-spying on Hong Kong protesters
Malware disguised as app geared towards protest movement was likely issued by the Chinese government, say Lacoon researchers
 Add ToI as a Preferred Source on Google
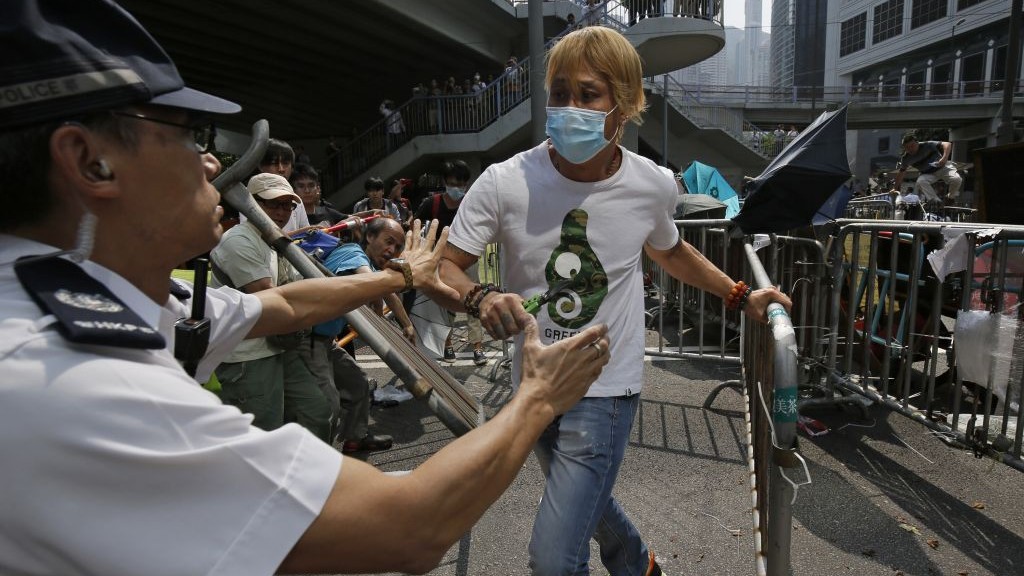
There’s a disturbing new twist in the confrontation in Hong Kong, where residents demand more freedom and the Chinese government pushes back. Israeli cyber-security firm Lacoon has discovered a new piece of spyware aimed specifically at protestors — apparently released by China itself. “The fact that this attack is being used against protesters and is being executed by Chinese-speaking attackers suggests it’s the first iOS Trojan linked to Chinese government cyber activity,” said Lacoon researchers Shalom Bublil, Daniel Brodie, and Avi Bashan in a blog post.
The Chinese malware, called Xsser mRAT (a RAT is a remote administration tool, a piece of software that allows a hacker to remotely control a device) was distributed several weeks ago via e-mail, Facebook, WhatsApp, and other social media platforms. Hong Kong news reports said activists received messages from a group called Code4HK, an advocacy hacker group working with protesters to improve government transparency in the territory. The messages urged activists to download an app to their smartphones which would update them on protest activities.
While the app did display some information, its main purpose was to siphon data, not present it, said the researchers. “After the victim presses the link in the WhatsApp message, an .apk file is downloaded. Once the user attempts to install the apk, the user is presented with an extensive permissions list that the apk needs,” the researchers wrote. “When the user first opens the app, a dialog box will prompt the user to update the app with the text ‘Application updates, please click to install.’ If the user agrees, the app is updated and the espionage capabilities are activated. Otherwise the application closes.”
The malware, which can extract just about any data on a device, is “undoubtedly one of the more advanced we’ve seen,” the researchers said. The fact that the mRAT appears in both Android and iOS flavors, and that both do the same thing – one of the few times such a cross-platform spying attack has ever been mounted, the researchers said – combined with “the identity of the victims, as well as data from the CnC (Command and Control) servers, lead us to believe that the Chinese government is behind the attack. This is also a very advanced mRAT that is undoubtedly being backed by a nation state,” they said.
“The Xsser mRAT is itself significant because while there have been other iOS Trojans found previously, this is the first and most advanced, fully operational Chinese iOS Trojan found to date. Although it shows initial signs of being a targeted attack on Chinese protesters, the full extent of how Xsser mRAT is being used is anyone’s guess. It can cross borders easily, and is possibly being operated by a Chinese-speaking entity to spy on individuals, foreign companies, or even entire governments,” the team noted.
Beijing has not commented on the accusations.

The Times of Israel Community.